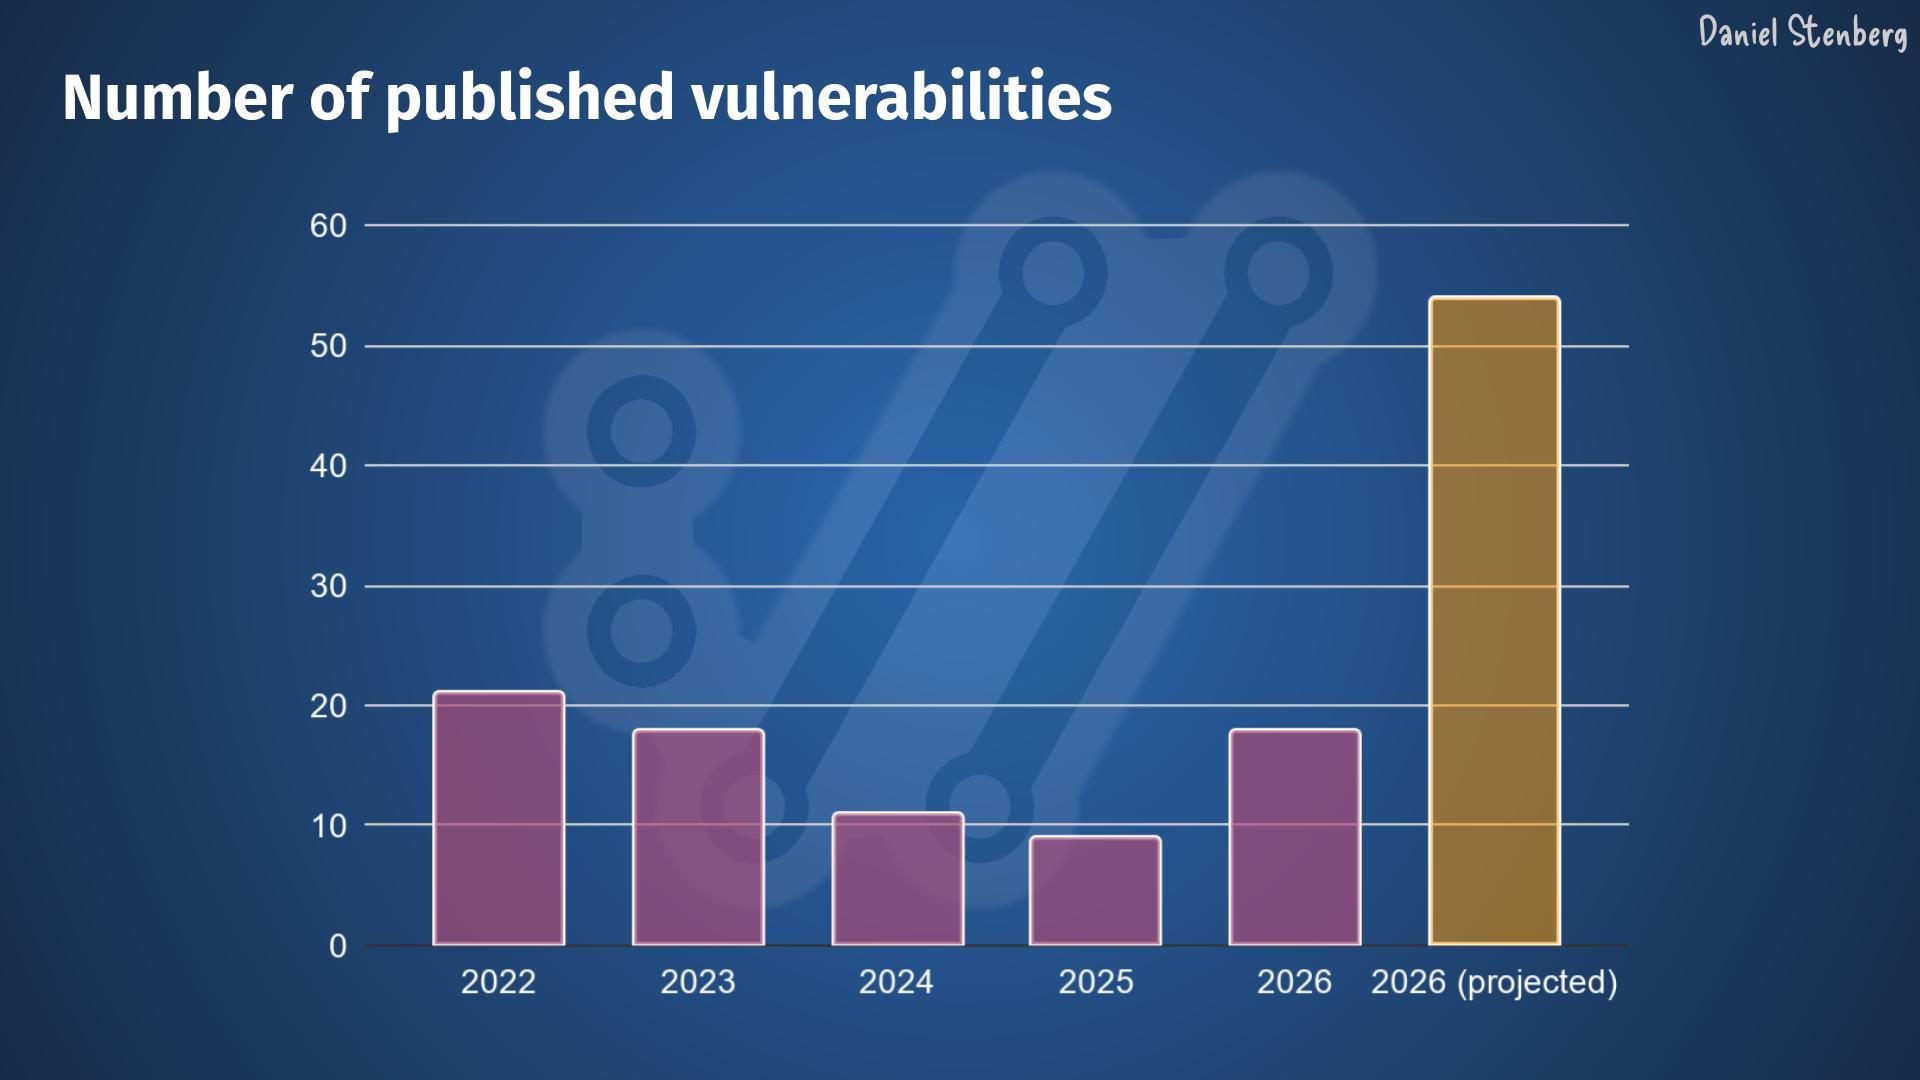
@bagder Surely, that projection isn't correct because there is a big batch of things being found now and it will dwindle down after that... Can we really expect multiple breakthroughs in tooling and breakthroughs in classes of vulnerabities this year?
@Varpie 1. the existing tooling is still being used to find more flaws not reported yet 2. there will be more tools created and used 3. all the tools will improve 4. we keep changing curl
So yes, I think it is a reasonable risk that the projection is correct.
Accessibility is certainly a general issue for FOSS projects. But in your case and given the popularity of the curl project (and yourself), I'd assume that vendors will keep lining up for your (implicit) endorsement.
Though I can imagine that ability / capacity might be a different story, with the number of new tooling and vendors entering this market every month.
@mechko@bagder@Varpie The problem is also that this situation is asymmetric: maintainers need to find every issue, reporters only need to find a single one. The way how LLM-based tools (or fuzzers for that matter) are working is better for the latter, especially as what is found depends on minor phrasing differences in the prompt and randomness. Two separate runs might find a different set of problems.
That said, it helps. It's not a panacea though as some people with monetary interests want to present it.